
ISACA
Germany Chapter
Expertise for responsible IT
ISACA is an international professional association for IT governance, IT audit, information security, risk and compliance. Its Germany Chapter brings these disciplines together through education, publications and professional exchange.
The COBIT framework helps link business objectives with accountable IT governance. The chapter’s qualifications offer further specialisation in governance, compliance and IT risk management.
My involvement combines membership and committee work with professional qualifications and publications. This brings practical methods and the perspectives of other professionals into my work.
The Germany Chapter combines international methods with local professional exchange. Working groups and events let practitioners share and develop experience in governance, audit, risk management and information security.
Areas of focus
- Governance and COBIT
- Information security and audit
- Knowledge sharing and networking
Connecting governance, compliance and security
Professional exchange that informs practice

Membership
Through the ISACA Germany Chapter, I exchange perspectives on governance, information security, audit and regulation and apply them in my work.

Committee work
On the Committee for Networks and Event Partnerships, I help develop events and partnerships that bring members and practitioners together.

Library
A contribution to the ISACA Journal and a book in the ISACA series connect governance methods with implementation, from measurement models to BYOD and compliance.
PROFESSIONAL ENGAGEMENT · IT GRC CONFERENCE
2027 Programme Committee
I help shape the programme for the 2027 IT GRC Conference. The committee sets the themes, reviews submitted contributions and helps select them. I bring my perspective on governance, compliance and information security to this work.
22–23 June 2027 · Rosengarten Mannheim · ISACA Germany Chapter × dpunkt.verlag
EXPERTISE IN PRACTICE
Turning governance into decisions
I bring governance, compliance and risk management together around a practical question: who makes which decisions, and what information do they need? COBIT provides a framework that can be adapted to the organisation.
Who decides what?
Clarify decision rights, responsibilities and escalation paths in line with business goals.
PRACTICAL DELIVERABLEResponsibility and decision model
How can requirements be managed?
Link regulatory obligations with risks, controls and traceable evidence.
PRACTICAL DELIVERABLEControl and evidence structure
Which metrics help leaders make decisions?
Turn IT objectives into a small set of reliable measures that support decisions and improvements.
PRACTICAL DELIVERABLEDecision-relevant measures
Insights from my practice
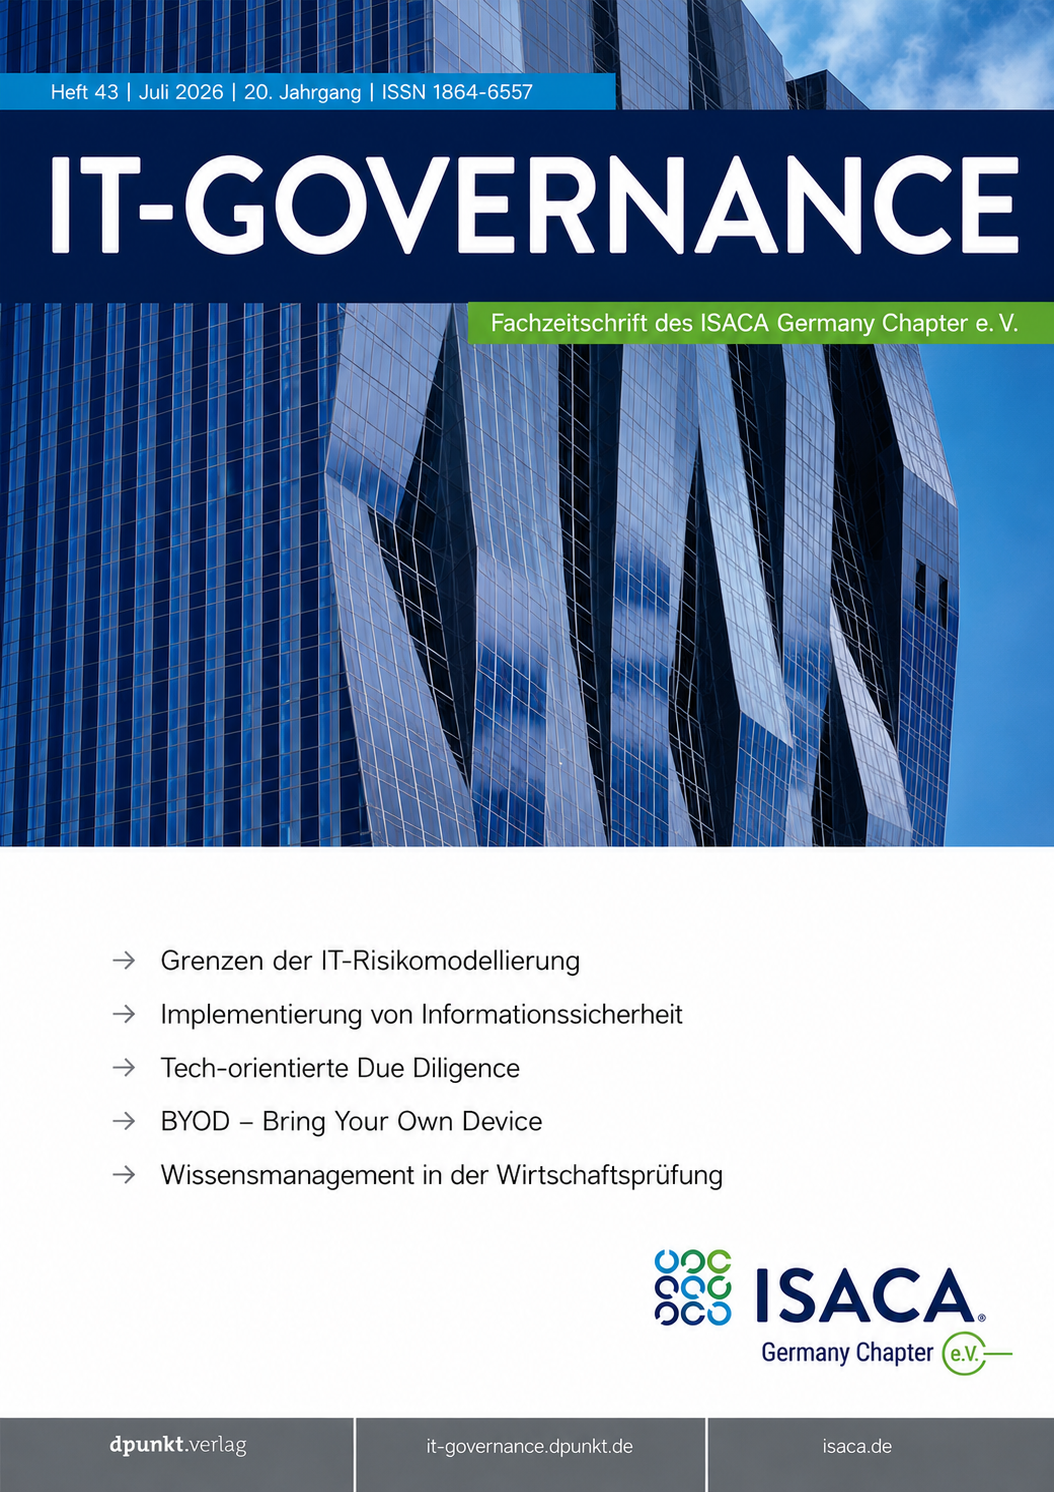
Making BYOD measurable
IT-Governance journal · Issue 43 / 2026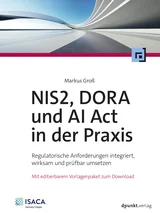
NIS2, DORA und AI-Act in der Praxis
Implement regulatory requirements in an integrated, effective and auditable wayBOOKS AND PUBLISHER TITLESBring governance, compliance and IT oversight together
Want to connect governance, compliance and IT oversight? Let’s discuss ownership, priorities and a practical next step.

